Lock down any MCP server or agent command with one word: Anthropic's srt sandbox, no container needed
TL;DR
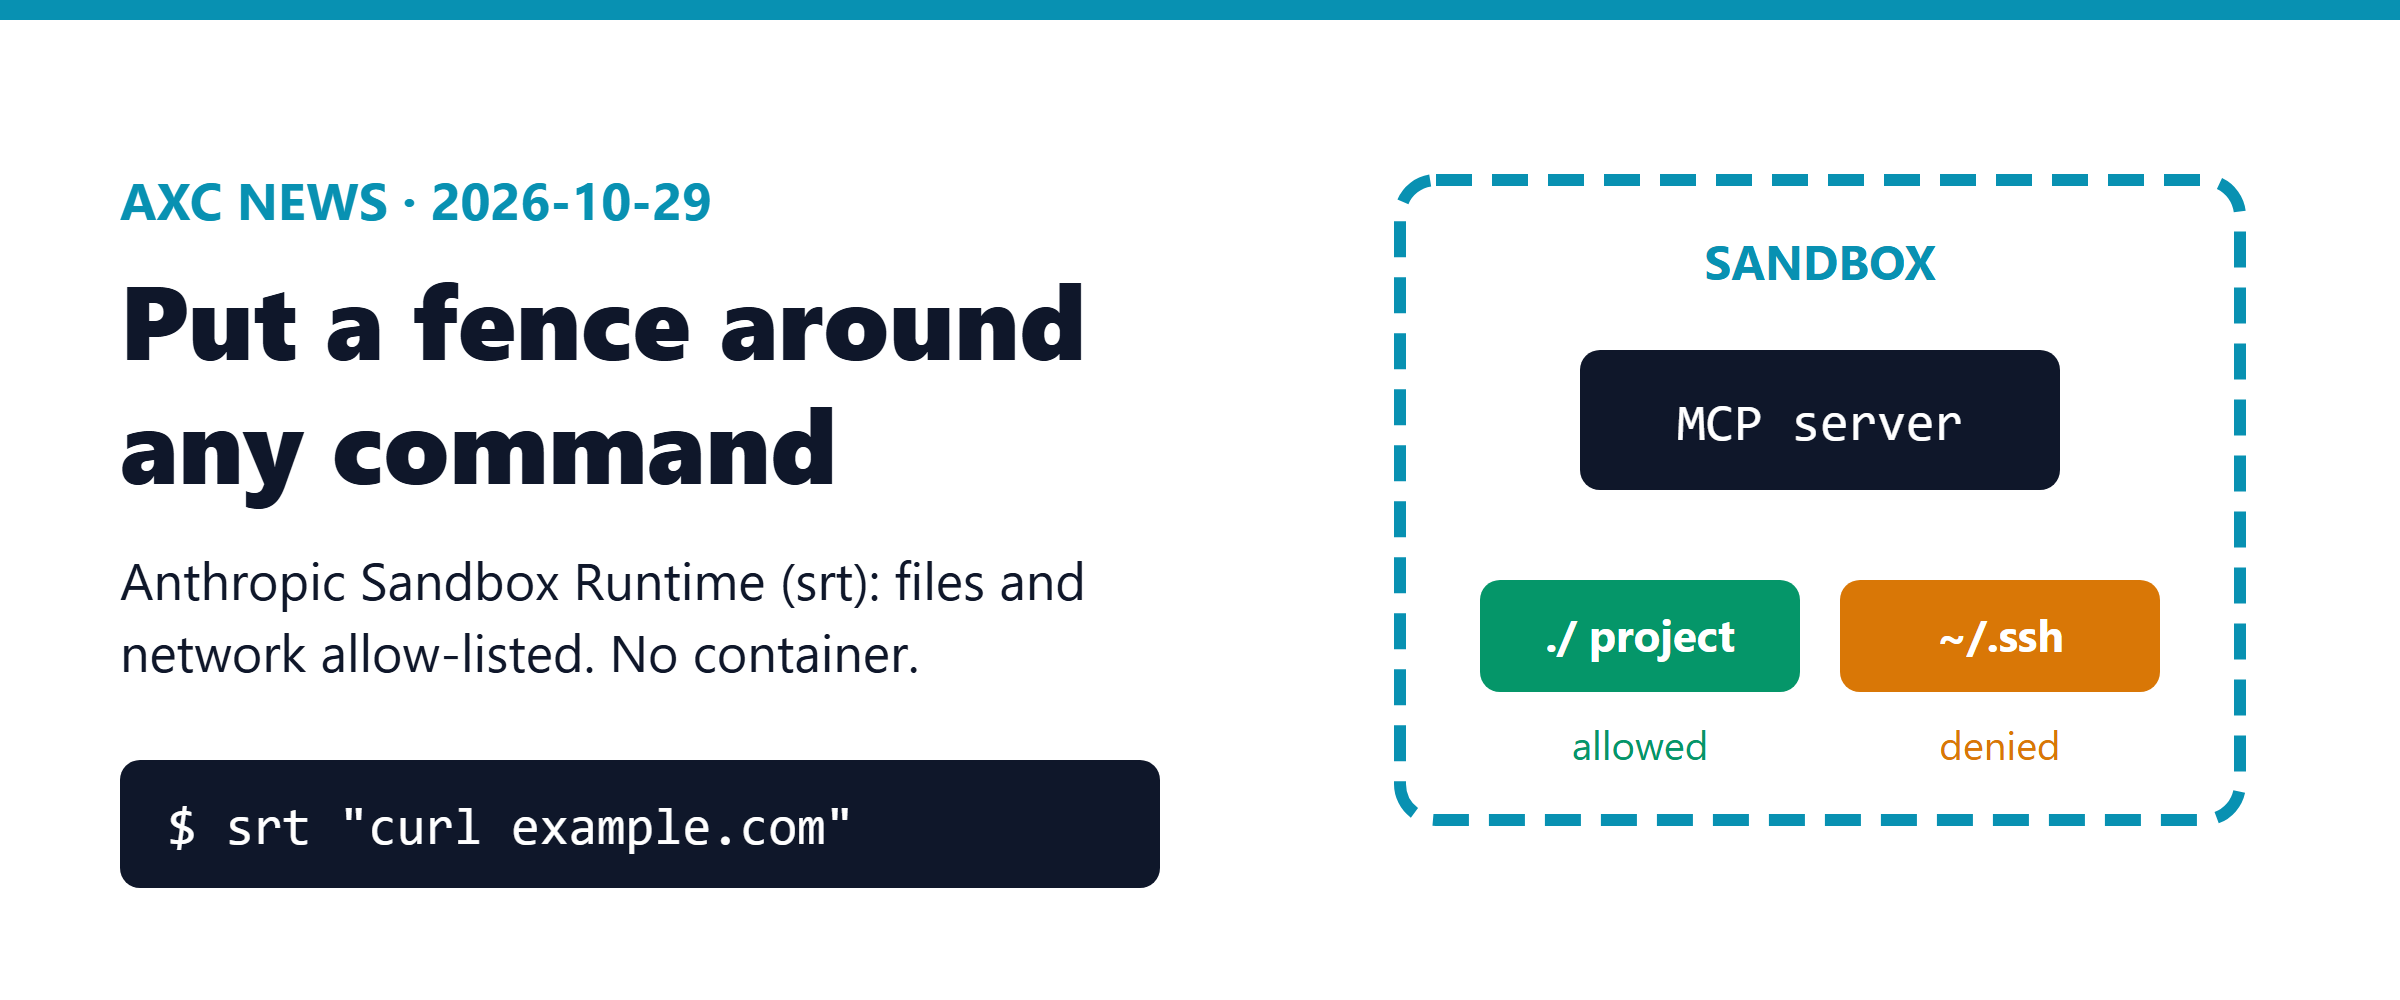
srtis Anthropic's open-source sandbox CLI, the same engine that Claude Code's/sandboxmode is built on.Put
srtin front of any command or local MCP server, and it can only touch the files and hosts you allow.One
npm install, one test command, one line changed in.mcp.json: about 5 minutes on macOS or Linux.
What it is
Every local MCP server you add runs as you. It can read ~/.ssh, your .env files, and send data to any host. You trust a stranger's npm package with all of that.
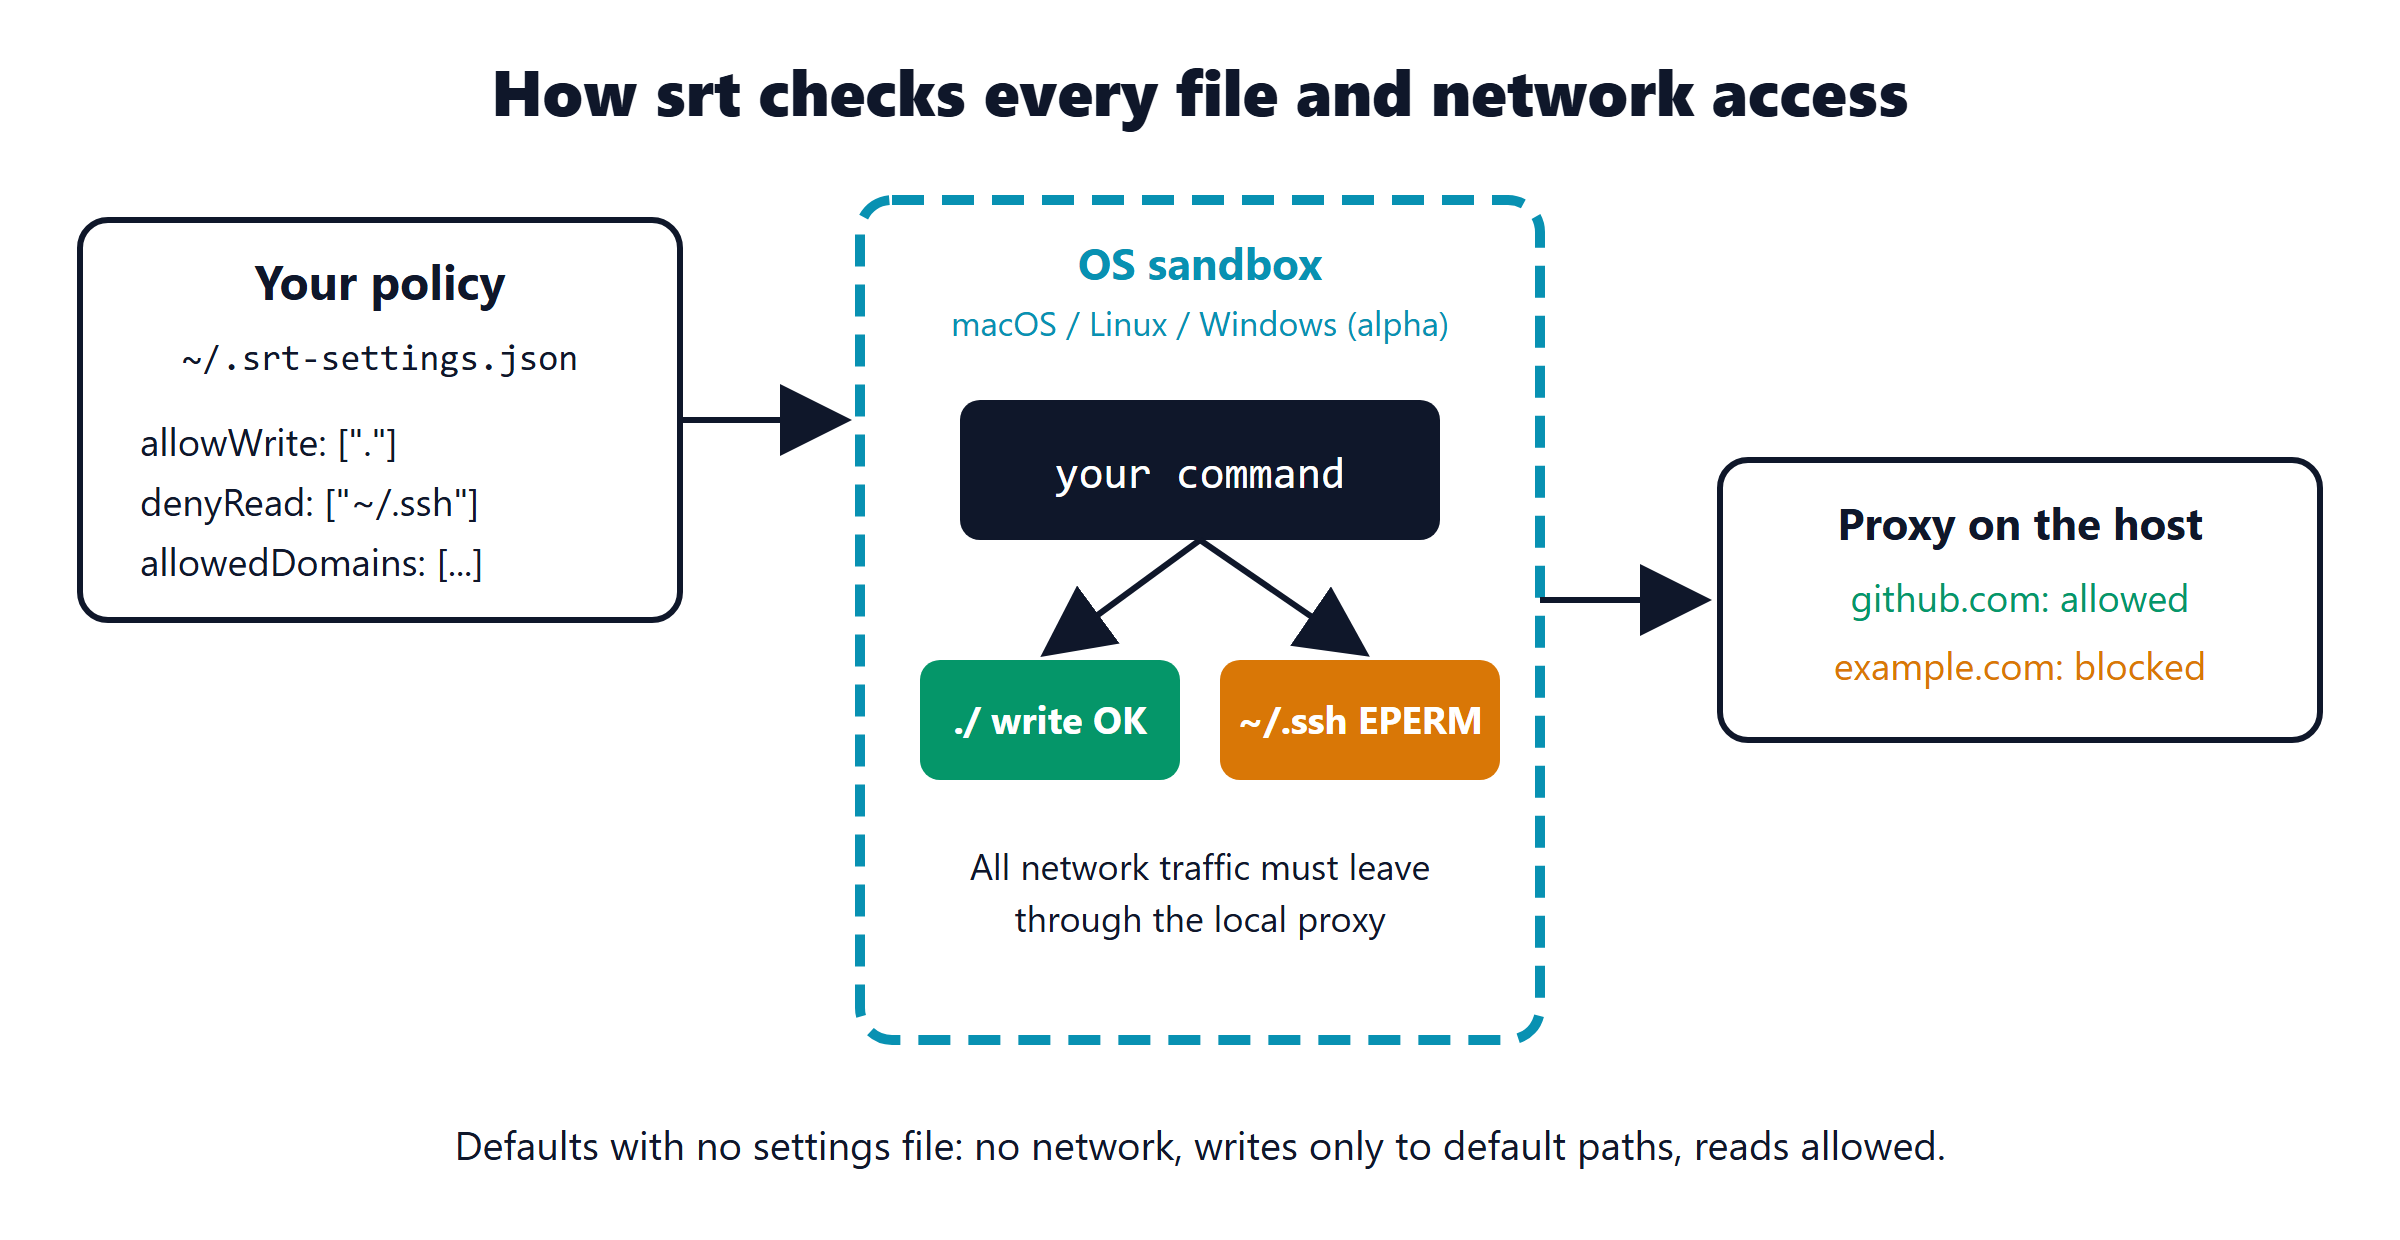
srt (Anthropic Sandbox Runtime) wraps a command in an OS-level sandbox: sandbox-exec on macOS, bubblewrap on Linux, and a dedicated local user account on Windows (alpha). There is no Docker image and no VM. You write the rules once in ~/.srt-settings.json: which folders it may write, which files it may not read, and which domains it may reach.
The repo appeared on GitHub's weekly TypeScript trending list this week (6,820 stars, +1,189 this week, checked 2026-10-29). The latest release, v0.0.81 (2026-10-20), hardens Windows with a write-restricted token. According to the Claude Code docs, "Claude Code builds the sandbox on the open source @anthropic-ai/sandbox-runtime package", so you are using the same engine directly.
Illustration
Try it in 5 minutes
Prerequisites: Node 22.12 or newer. macOS: brew install ripgrep. Linux: bubblewrap, socat and ripgrep (for example sudo apt-get install bubblewrap socat ripgrep). Windows (alpha): run npx @anthropic-ai/sandbox-runtime windows-install once, which asks for admin rights.
Step 1: Install
npm install -g @anthropic-ai/sandbox-runtimeStep 2: Run a command inside the sandbox
srt "curl example.com"With no settings file, srt uses its defaults: no network access, no writes outside the default write paths, and reads allowed. So the request is blocked.
Step 3: Sandbox your MCP server
In .mcp.json, set "command": "srt" and move the old command into args:
{
  "mcpServers": {
    "filesystem": {
      "command": "srt",
      "args": ["npx", "-y", "@modelcontextprotocol/server-filesystem"]
    }
  }
}
Then write your policy in ~/.srt-settings.json (example from the README):
{
  "network": { "allowedDomains": ["github.com", "*.github.com"], "deniedDomains": [] },
  "filesystem": { "denyRead": ["~/.ssh"], "allowWrite": ["."], "denyWrite": [".env"] }
}
What you will see: step 2 prints Connection blocked by network allowlist, and the MCP server gets Operation not permitted (EPERM) when it touches a path your policy denies.
Tip: A settings file that exists but is empty or invalid is an error.
srtrefuses to run instead of silently falling back to the defaults. Keep the file valid JSON.
Caveats
Beta research preview. The README says APIs and the config format may still change. The version is 0.0.x.
Broad domains leak. Allowing
github.comalso allows uploads to GitHub. The README warns about exfiltration and domain fronting.Windows is alpha. It needs a one-time admin install and has known gaps (SMB shares, WSL and some token tricks are not fenced). Claude Code's own
/sandboxis not available on native Windows; use WSL2.Install it outside the project. A copy in
<project>/node_modules/can be rewritten by the sandboxed command. Usenpm install -gornpxfrom outside the project.Not for everything. Tools that ignore
HTTP_PROXYon Linux cannot connect, and Jest needs--no-watchman.
Claude Quick Hits
Claude Enterprise admins get smart reports, surveys and pooled group budgets (2026-10-28): claude.com
AI Tool Radar
Repo/Tool | What it does (1 line) | Stars (growth) | Quick try |
|---|---|---|---|
Official AWS plugins, skills and MCP server for coding agents (Apache-2.0) | 3,332 (+408 this week) |
| |
Self-hosted, persistent AI teammates with their own computers; beta, v0.3.6 (2026-10-28) | 6,156 (+1,094 this week) | Read the self-host guide in the README first |
Sources
https://github.com/anthropics/sandbox-runtime
https://github.com/anthropics/sandbox-runtime/releases/tag/v0.0.81
https://www.npmjs.com/package/@anthropic-ai/sandbox-runtime
https://code.claude.com/docs/en/sandboxing
https://github.com/trending/typescript?since=weekly
https://github.com/aws/agent-toolkit-for-aws
https://github.com/elie222/rakazo
https://claude.com/resources/articles/smart-reports-surveys-pooled-budgets